

appsec.study
A set of deliberately vulnerable machines, grouped by the skill each one exercises, for practicing web application security testing.
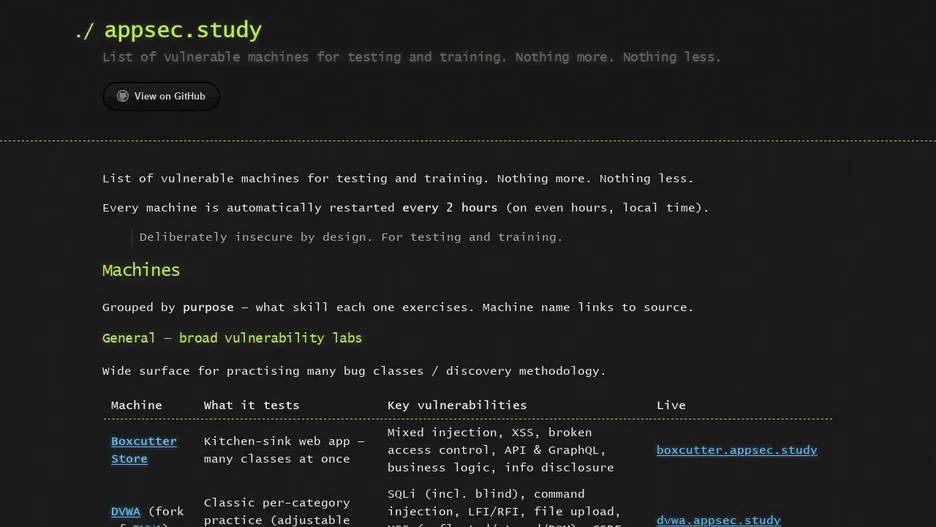
appsec.study is a list of deliberately insecure machines for security testing and training, each restarted automatically every two hours. Machines are grouped by purpose: general labs with a wide mix of vulnerability classes, a DVWA fork for classic per-category practice, an artifact-recovery box built around leaked Git history, and API-focused targets covering REST and GraphQL flaws such as BOLA/IDOR, broken function-level authorization, mass assignment, SSRF, SQL injection, weak JWTs, XXE, SSTI and open redirects.
Other machines focus on realistic business-logic bugs, such as a feature-rich casino app where wallet, deposit, promo and RNG flaws are hidden among roughly fifty correctly built features. Each machine's page links its vulnerability classes and, where relevant, its source.
It is written in JavaScript.