

CHAI
An autonomous penetration-testing MCP server with an integrated AI decision engine, designed to run on a Raspberry Pi running Kali Linux ARM64 and chain pentest tools with minimal LLM calls.
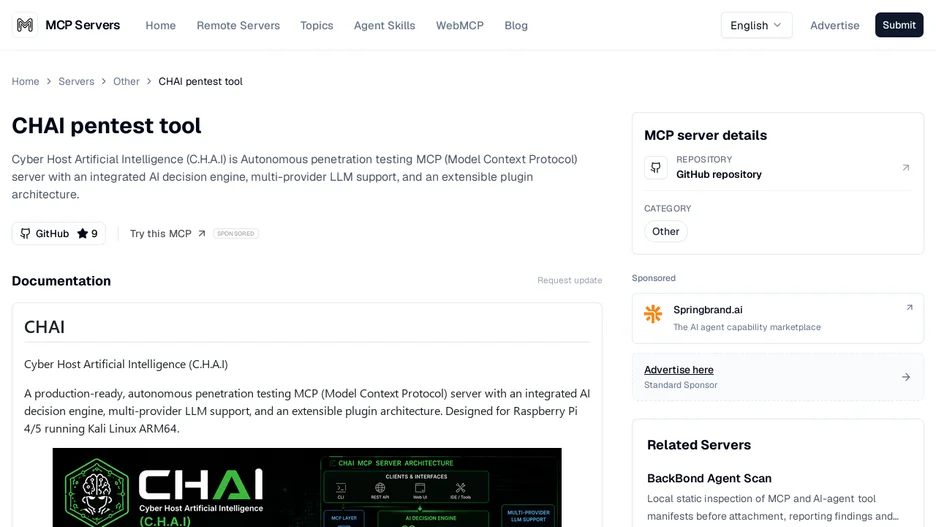
CHAI follows a thin-brain, thick-loop design: an internal LLM fires only at decision boundaries, deciding what to test next, whether to continue, and how to summarize findings, while a local execution loop handles tool chaining deterministically between LLM calls, keeping token usage to roughly 6 to 10 calls per full pentest and latency acceptable on a Raspberry Pi 4.
It supports multiple LLM providers, including Azure OpenAI, direct OpenAI, Anthropic Claude, Amazon Bedrock, OpenRouter and HuggingFace-hosted models. Sandboxing uses firejail profiles with resource limits, Linux cgroups, a restricted execution user, a tiered safety policy and immutable audit logging of every command and AI decision. A plugin system auto-discovers bundled and external plugins, with Feroxbuster, Metasploit and the Burp Suite API included out of the box.
Findings are stored in SQLite with a knowledge graph of more than 50 attack techniques queried through recursive queries, avoiding a dependency on Neo4j, Redis or Postgres. It targets Raspberry Pi 4 or 5 running Kali Linux ARM64 on bare metal, without Docker, and requires Python 3.11 and firejail.