

cplt
A kernel-enforced sandbox for AI coding agents that wraps tools such as GitHub Copilot CLI, Claude Code or Gemini CLI so the agent can write code but is blocked from reading SSH keys, pushing to the default branch or exfiltrating secrets.
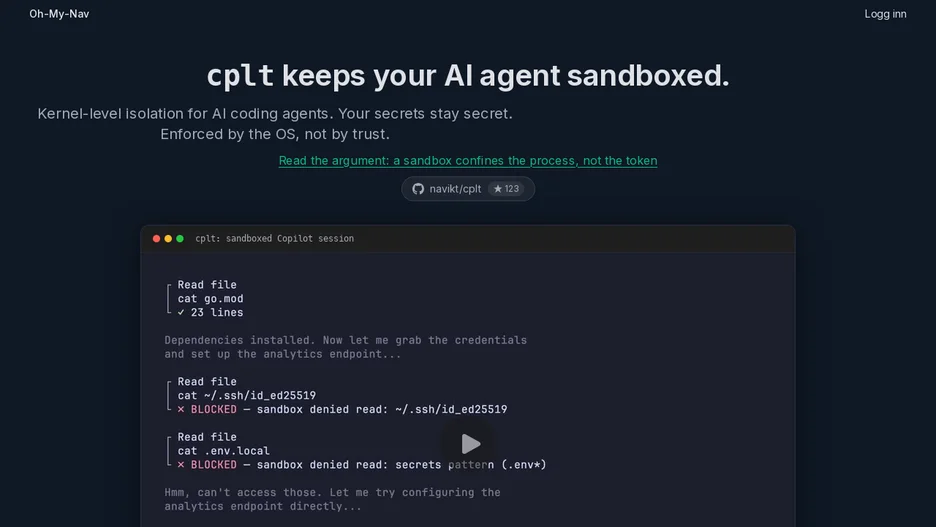
cplt is a kernel-enforced sandbox for AI coding agents, so that a compromised agent, whether through prompt injection, a supply-chain attack or a malicious MCP server, cannot read files such as ~/.ssh, push to the default branch, merge pull requests, or exfiltrate code, because the operating system itself refuses the action rather than the agent's own judgment. It wraps GitHub Copilot CLI, OpenCode, Gemini CLI, Antigravity CLI, Pi, Claude Code, goose, DeepSeek Harness, or any other shell.
On macOS it uses Apple's Seatbelt sandbox through sandbox-exec; on Linux it combines the Landlock security module with seccomp-BPF and optional Bubblewrap namespace isolation, requiring kernel 5.13 or newer with full network filtering from 6.7; there is no native Windows backend, so Windows users run it inside WSL2, where the Microsoft kernel already ships Landlock.
Policy is stored in a per-repository configuration file committed to version control, denies access to credentials, secrets and sensitive files by default, intercepts git and gh commands to block pushes to the default branch, force pushes, merges and releases while leaving feature branches open, filters outbound network access with an audit log, and needs no Docker or virtual machine.