

Nasiko
A single control-plane process that deploys, routes, secures and observes A2A-speaking AI agents behind one gateway, with an LLM router that never exposes a real API key to an agent.
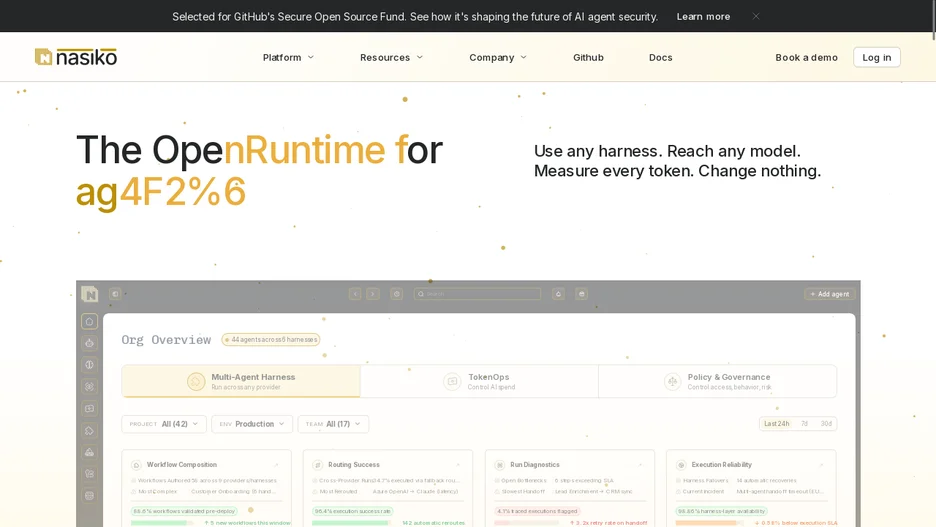
Nasiko is a single control-plane process that sits in front of a fleet of agents speaking the A2A protocol, deploying, routing, securing and observing them without a separate gateway, sidecar or glue code. It terminates TLS, authenticates every request, and proxies all agent-to-agent traffic itself, so agents are never publicly reachable and every hop is a checkpoint for rate limits, access control and tracing.
A deploy command builds and runs any A2A-speaking agent against an embedded registry, and a three-stage routing engine shortlists agents by embedding similarity, reranks them on conversation context, and makes a final pick with an LLM. An MCP gateway gives every agent one permission-filtered view of Composio toolkits and custom MCP servers without holding credentials itself, and an LLM router hands an agent a short-lived identity token instead of a real API key, resolving the provider, model and key on the server side.
Every dispatch and proxy hop emits an OpenTelemetry span with token usage and cost collected automatically, and Redis-backed flow guards limit call depth, fan-out, token budget and timeout to stop runaway agent loops. It works with agents written in Python, Rust, Go or TypeScript, and is written in Rust.