

RAGdrag
A command-line toolkit for security-testing Retrieval Augmented Generation pipelines, covering 27 techniques across six kill-chain phases mapped to MITRE ATLAS, from detecting a RAG pipeline to exfiltrating or poisoning its knowledge base.
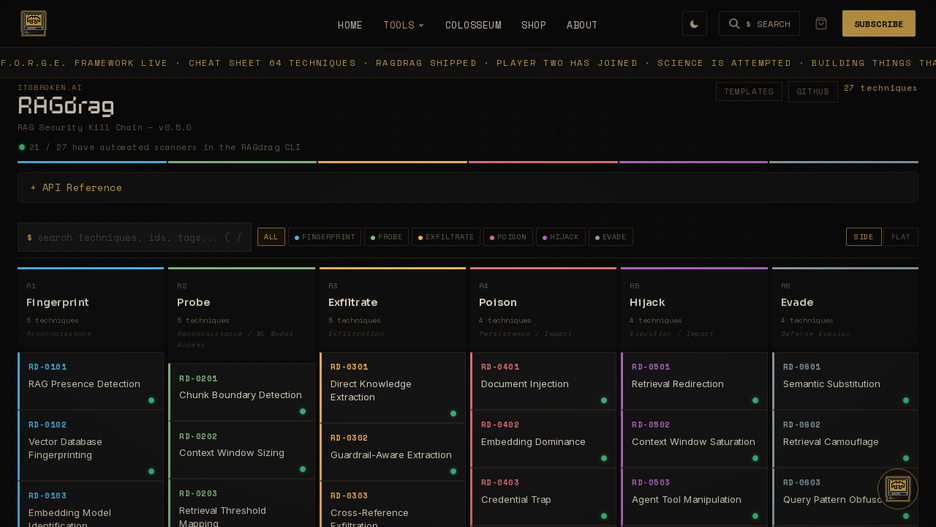
RAGdrag treats a RAG pipeline as its own assessment surface rather than just another LLM to prompt-inject, with recon, data-exposure, poisoning and evasion techniques specific to retrieval systems. It organizes 27 techniques into six kill-chain phases mapped to MITRE ATLAS: fingerprinting a RAG deployment and its vector database, probing pipeline internals such as chunk sizing, extracting knowledge-base contents and credentials, injecting attacker-controlled content, hijacking retrieval and generation, and testing evasion against guardrails and monitoring.
It installs with pip and is pointed at any RAG-enabled endpoint with no further setup. A separate companion repository provides intentionally vulnerable lab servers, built on Ollama, for practicing against without a live target.
Individual commands run one phase at a time, a scan command runs several phases together, a listen command starts a credential-capture HTTP listener for techniques that rely on callbacks, and a report command turns findings into JSON.