

sandbox
Fast-booting MicroVM sandboxes for AI agents, with warm pools for near-instant claims, a per-node control plane, and Go and Python SDKs for executing commands and files inside the guest.
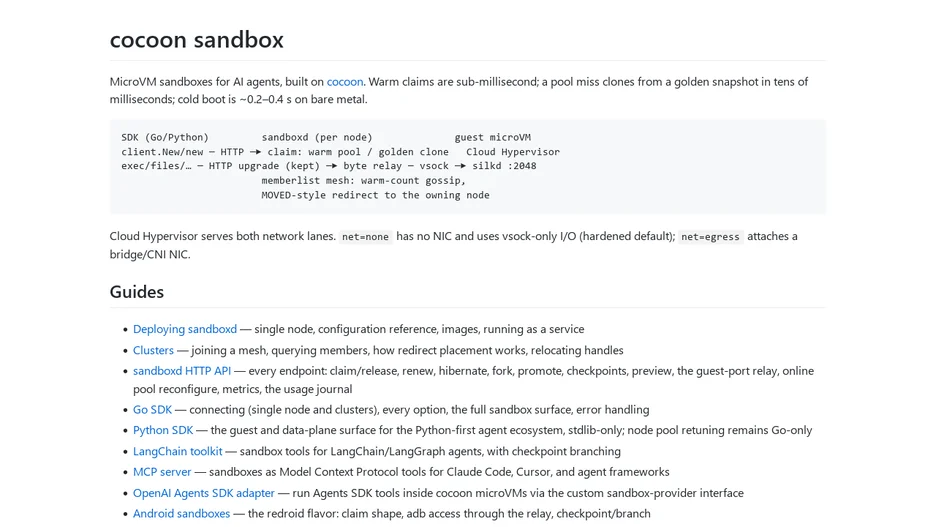
sandbox provides MicroVM sandboxes for running AI agent actions in isolation, built on a project called cocoon. A per-node control plane keeps a warm pool of pre-booted virtual machines so claiming one is sub-millisecond, falls back to cloning from a golden snapshot in tens of milliseconds on a pool miss, and can cold-boot a fresh one in a fraction of a second on bare metal.
Each guest runs an in-guest daemon that exposes command execution with context, persistent shell sessions, streaming file transfer, git operations, port forwarding and a language-server broker over a vsock connection, reached through a per-node control plane that handles claiming, releasing, forking, checkpointing and hibernating sandboxes, with usage and audit logging. It ships Go and Python SDKs for driving sandboxes from code, an MCP server that exposes the same surface as tools for Claude Code, Cursor and other agent frameworks, and adapters for the OpenAI Agents SDK and LangChain.