

ShipProof
A local-first production evidence gate that scans a repository for security, correctness, scale and performance issues without executing its code.
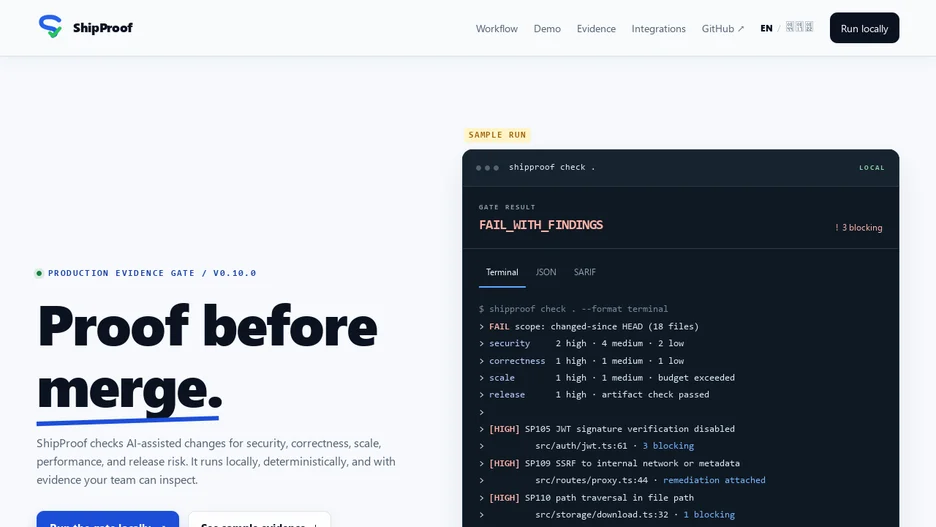
ShipProof scans source code without running it, evaluates measured CPU, RAM and latency budgets, checks reviewed capacity assumptions, and emits evidence through terminal output, JSON, SARIF, a pre-commit hook, GitHub Actions, or an optional read-only MCP adapter. It targets repositories written by people, coding agents, or both.
The project states it is not a certification, penetration test, formal proof, or substitute for product-specific threat modeling and runtime tests; instead it makes assumptions visible and reports the strength of its evidence. A bundled demo API contains five real vulnerable code paths that the scanner flags, with a test suite verifying the before/after contract.
The CLI runs via npx or a global npm install, and can scaffold repository-scoped skills for Codex and Claude Code. Node.js 20+ runs the CLI; Python 3.10+ is needed for the scan, check and gate commands.