

DefenseClaw
A security-governance layer for OpenClaw and other agentic AI runtimes that scans capabilities before use, inspects runtime traffic, and exports durable audit evidence.
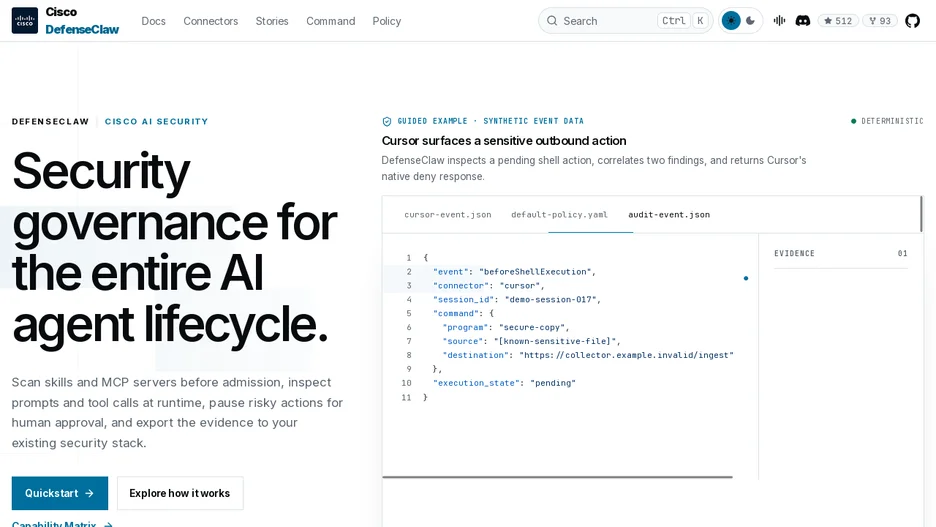
DefenseClaw is a security-governance system for agentic AI runtimes such as OpenClaw, combining a Python operator CLI, a Go gateway, connector hooks, policy definitions, scanners and observability exporters into one enforcement and evidence layer. It scans a capability before it is used, inspects traffic at runtime, and exports durable audit evidence, though the project states plainly that it does not itself prove an agent or third-party capability is free of risk.
Its documentation website is the canonical source for installation, configuration, CLI reference, connector compatibility and guardrail setup; the repository's own markdown is limited to contributor guidance and internal design records. Building from source requires Python 3.10 to 3.13 and Go 1.26.4, with a make build target that produces checkout artifacts without changing an already-installed system.