

ToolTrust Scanner
A static security scanner that grades MCP tool definitions A through F for risks such as prompt injection, data exfiltration, privilege escalation, and supply-chain backdoors, before an agent is allowed to call them.
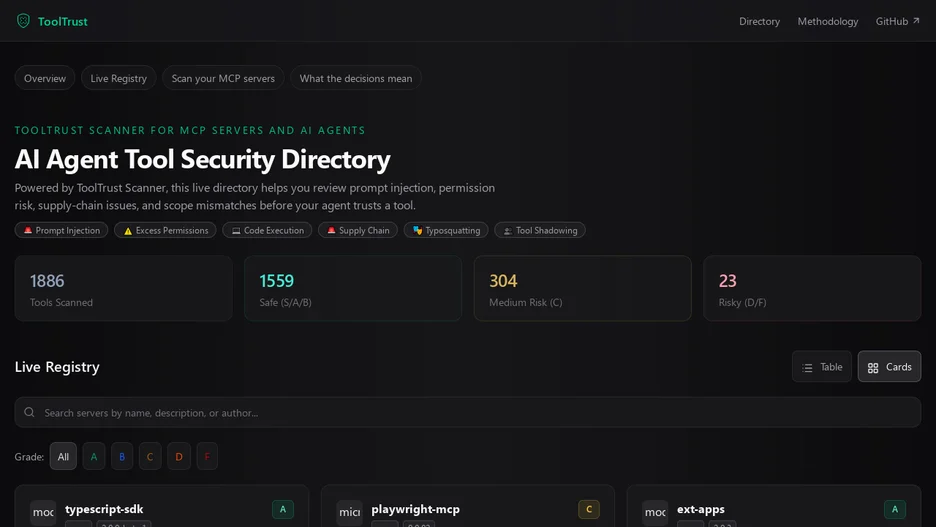
ToolTrust Scanner is a static security scanner for Model Context Protocol tool definitions, run as an MCP server, a CLI, or a CI check rather than as a host, gateway, or runtime proxy. It scans tool definitions before an agent trusts them and assigns each one a trust grade from A to F, since every MCP tool an agent can call is a potential attack surface for prompt injection, data exfiltration, privilege escalation, or a supply-chain backdoor.
Added as an MCP server, it lets an agent scan its own configured tools and return a risk report with grades and enforcement decisions in seconds; a CLI and a curl-based installer are also provided. It runs 16 static tool-definition rules plus 2 source-scan rules for embedded MCP implementations in this repository, and a public directory site aggregates grades and trends across scanned MCP servers, reporting from one published research pass that only about 10 percent of 207 scanned servers had a clean grade A.
It is written in Go and distributed under the MIT license.